Iran's quiet war inside Israel's networks- 281
July 10, 2026
While Israeli and American forces struck Iranian targets from the air, a quieter campaign was already running
Beneath the Radar: A Reawakened Espionage Toolkit Targets Southeast Asian Governments- 256
July 18, 2026
For over a year, an intrusion set moving through government and diplomatic networks across Southeast Asia left
North Korea just made its malware payload host itself on the blockchain- 252
July 5, 2026
North Korean threat actors behind the long-running Contagious Interview campaign have distributed more than 100 malicious
China-Linked CL-STA-1062 Shifts From Taiwan to Critical Infrastructure Across Southeast Asia- 249
July 1, 2026
A China-linked threat group that spent years quietly attacking Taiwanese web-hosting infrastructure has, over the
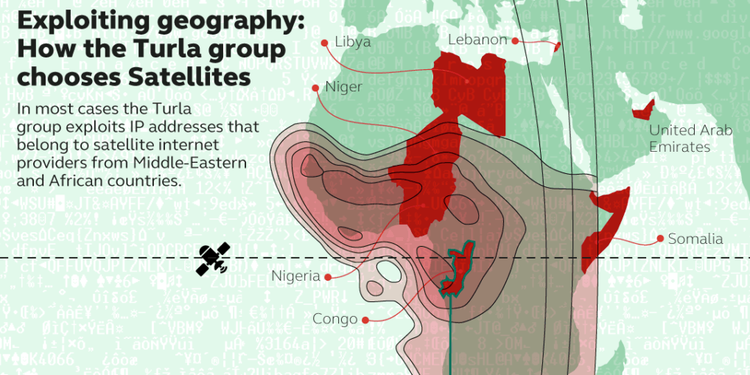
Turla's botnet redesign is about surviving disruption, not just evading detection- 240
June 28, 2026
Russia's FSB-linked Turla group has rebuilt its longstanding Kazuar backdoor into something structurally different
Patient by Design: FrostyNeighbor's Return and the Human Operator as Evasion Mechanism- 205
June 19, 2026
Most malware tries to avoid detection by being technically sophisticated. FrostyNeighbor avoids detection by being patient. Its
Nothing to See Here: The Cyber Sabotage Framework That Preceded Stuxnet by Five Years- 202
June 24, 2026
The historical understanding of offensive cyber operations is being re-evaluated following the discovery of a sophisticated
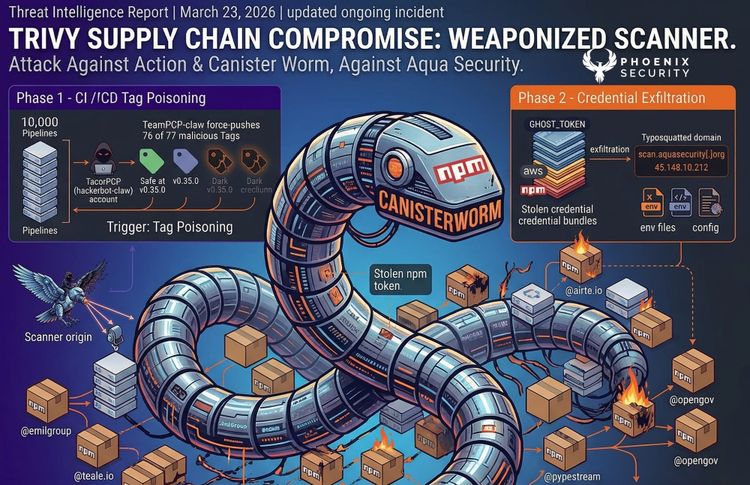
The Worm in the Toolchain: How TeamPCP Built a Credential Extraction Economy Inside Open Source- 201
June 23, 2026
The most consequential credential theft does not happen when a user clicks a phishing link. It happens
The Long Game: How China's Cyber Harvest Became a Western Intelligence Priority- 199
June 19, 2026
A significant shift has occurred in how Western nations characterize Chinese cyber operations, moving away from quiet
The Art of Looking Innocent: Iran's Dual-Track Tradecraft Evolution- 198
June 23, 2026
Iran's most effective cyber operations in 2026 do not announce themselves. One looked like routine