The Slow Breach: How Long an Attacker Sat Inside South Korea's Diplomatic Training Academy- 324
August 1, 2026
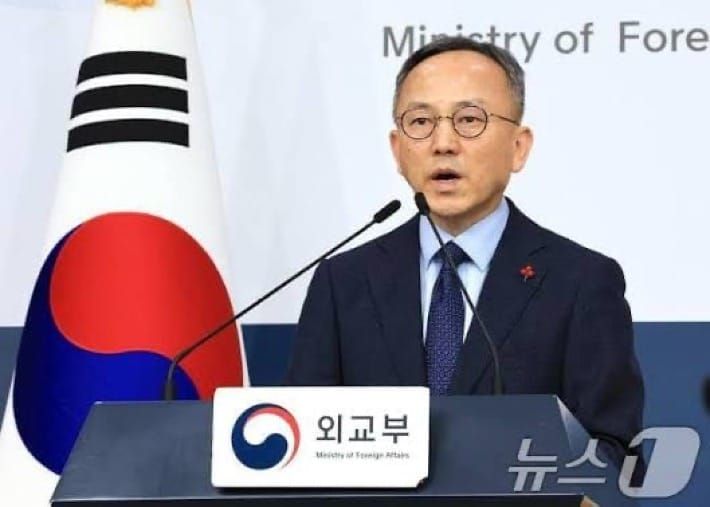
South Korea's Ministry of Foreign Affairs confirmed this month that a cyberattack against the Korea National Diplomatic Academy exposed data on a "considerable scale," while acknowledging that investigators are still working out both the full extent of the compromise and, more strikingly, still lack the technical evidence needed to say who was responsible. Ministry spokesperson Park Il told reporters that foreign state-backed involvement has not been ruled out, but stopped short of naming a suspect — a level of public uncertainty that, on a case involving a country's own diplomatic training institution, says as much about the difficulty of the investigation as it does about the sensitivity of what may have been taken.
What the ministry has confirmed is the shape of the intrusion rather than its author. Attackers exploited a previously unknown zero-day vulnerability, combined with existing security configuration weaknesses, to infiltrate the academy's online education platform — the system KNDA uses to deliver coursework and manage administrative functions for the diplomats who pass through it. According to the ministry's own timeline, the attacker gained control of a server sometime between April and May of 2025 and retained that access until February 2026, a window of roughly ten months during which the intrusion went undetected by the academy itself. It was eventually discovered only after a separate government agency flagged suspicious activity, at which point authorities moved to block the compromised system. The platform housed both educational content and the administrative information required for course management, including participants' names and user IDs — though officials have been candid that determining exactly what was accessed or exfiltrated during a ten-month dwell time remains genuinely difficult, a limitation worth taking at face value rather than reading as reticence.
South Korean newspaper Dong-A Ilbo, citing government sources, reported a figure the ministry itself has not officially confirmed: personal information belonging to nearly 6,000 current and former diplomats, along with officials seconded to the academy from other ministries, may have been compromised. The same reporting noted that intelligence agencies are specifically examining whether a hacking group linked to North Korea could be responsible, a line of inquiry that follows naturally from what the exposed data actually consists of — information tied to diplomats posted overseas is precisely the category of intelligence a state adversary would value most, useful for identifying individuals, mapping postings, and potentially supporting further targeting of South Korean personnel operating abroad. That the ministry has not confirmed this attribution publicly, even as domestic press reporting points toward it, is consistent with the broader caution officials have shown throughout the disclosure: preliminary findings, an unconfirmed scale, and an explicit acknowledgment that the investigation remains ongoing.
What ties this case to a wider pattern is less any single technical detail than the timeline itself. A zero-day vulnerability bought the attacker initial entry, but it was the combination with unaddressed configuration weaknesses that let a foothold on one server persist, undetected, for the better part of a year — inside an institution whose entire function is training the country's next generation of diplomats, and whose compromise, if it does trace back to a hostile intelligence service, would represent a textbook use of cyber intrusion for old-fashioned human intelligence collection: not disruption, not extortion, but quiet, patient access to exactly the roster of people a foreign service would most want to know about. Park Il said the ministry is now coordinating with relevant government agencies both to determine the full scope of what happened and to strengthen internal cybersecurity to prevent a repeat — a response that, ten months after the intrusion actually began, is arriving well after whatever value the access held for its author had already been extracted.